We currently support a group of medical technology organisations as their fractional vCISO. We have led supplier risk reviews, strengthening vendor onboarding, and creating a practical roadmap to achieve Cyber Essentials Plus certification.
We help organisations turn complex cybersecurity challenges into practical improvements, with work spanning strategy, research, implementation, and assurance.
We currently support a group of medical technology organisations as their fractional vCISO. We have led supplier risk reviews, strengthening vendor onboarding, and creating a practical roadmap to achieve Cyber Essentials Plus certification.

We delivered a presentation to a broad range of small and medium sized companies on a sensible and affordable approach to cybersecurity. This work also resulted in a whitepaper.
We deliver technical papers and presentations on emerging cybersecurity issues. Recent topics included a detailed technical paper on the impact of mobile application store changes, .

We designed and deployed a new Microsoft 365 environment for a non-profit operating in a high-risk industry, overseeing migration, configuration, and Defender and Purview hardening under E5 licensing.

When the broadband for a luxury property kept being disabled by their ISP because of suspicious traffic patterns, we completed internal and external network scans and testing. This identified an unpatched CCTV system that had been compromised, which we could disconnect and advise on replacing. Whilst there we also helped the client improve their network design and approach to patching.
We test Microsoft 365 and Google Workspace environments against common security benchmarks. Recent tests have looked at tenants with a wide range of maturity levels, from a high-level review of the key security controls as part of a general review, to in-depth testing of well established tenants.
We work with startups, scale-ups, and medium-sized businesses across a range of technology, advisory, and non-profit sectors:
We want our customers to see us as a trusted, long-term technology and cybersecurity partner.
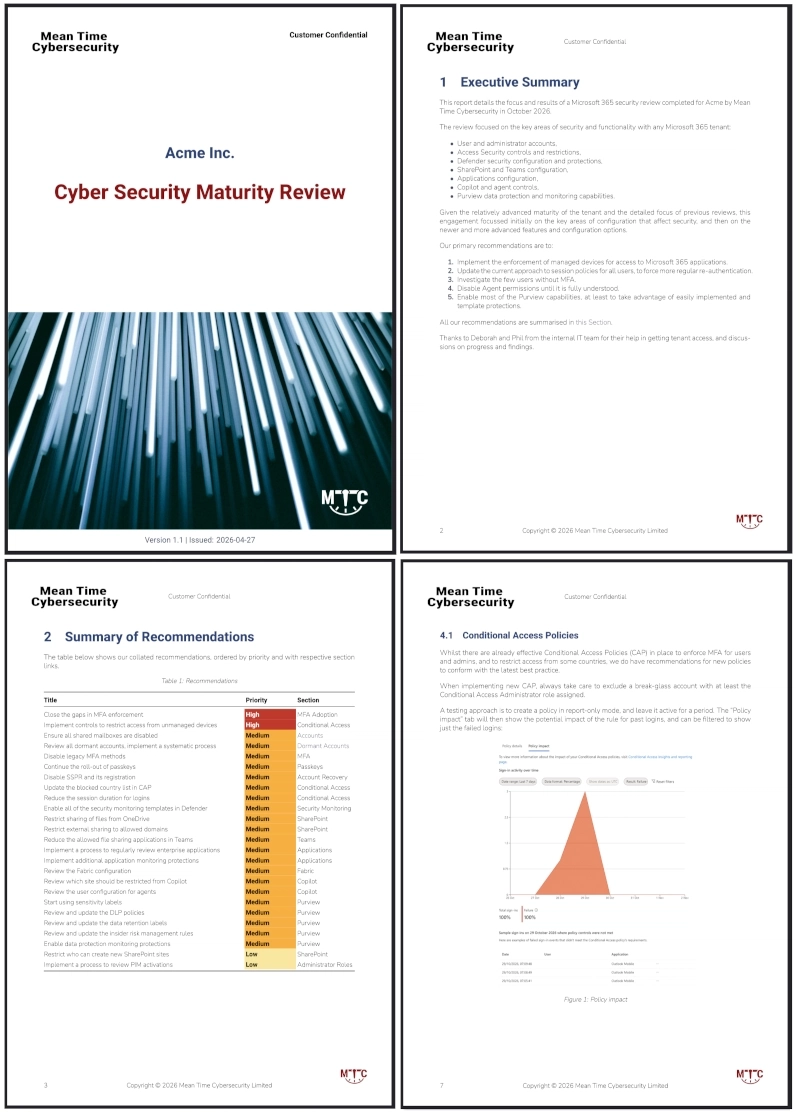
For testing engagements and reviews our reports contain the full details needed to explain and reproduce an issue, and pragmatic advice on remediation. They also typically include an executive summary and a prioritised list of recommendations:
We do not look for commodity engagements where we drop a report and walk away; many of our smaller customers have us plan and implement improvements too. The result is more than a report; it’s also a more secure and trustworthy system.